DORA for everyone: financial entities and ICT providers.
The Digital Operational Resilience Regulation has applied since January 2025. You start from a questionnaire that adapts to your type of business, with an ICT provider register and an incident register ready.
You say who you are, and what does not concern you is removed.
At the start you answer a few yes or no questions. A bank, an insurer, a payment institution, a fund or a cloud provider get the same template, but each sees only their own requirements.
Financial entities
Banks, insurers, investment firms, payments and e-money, fund managers, pension funds, crypto-asset providers. With the points for incidents, testing, TLPT and third-party providers.
ICT providers
Software houses, cloud, hosting and managed services working for the above. Your clients ask you for clauses, incident notification, audit and an exit plan. Here you prepare the answers.
Small businesses
If you fall under the simplified framework, you declare it and the advanced tests are removed. The basics remain, according to your size.
Everything the regulation asks for, in eleven sections.
Each question refers to its article and asks for the documents an auditor will look at.
ICT governance and risk
Management approval, roles, yearly review, framework audit, backups, continuity and recovery.
Incidents and reporting
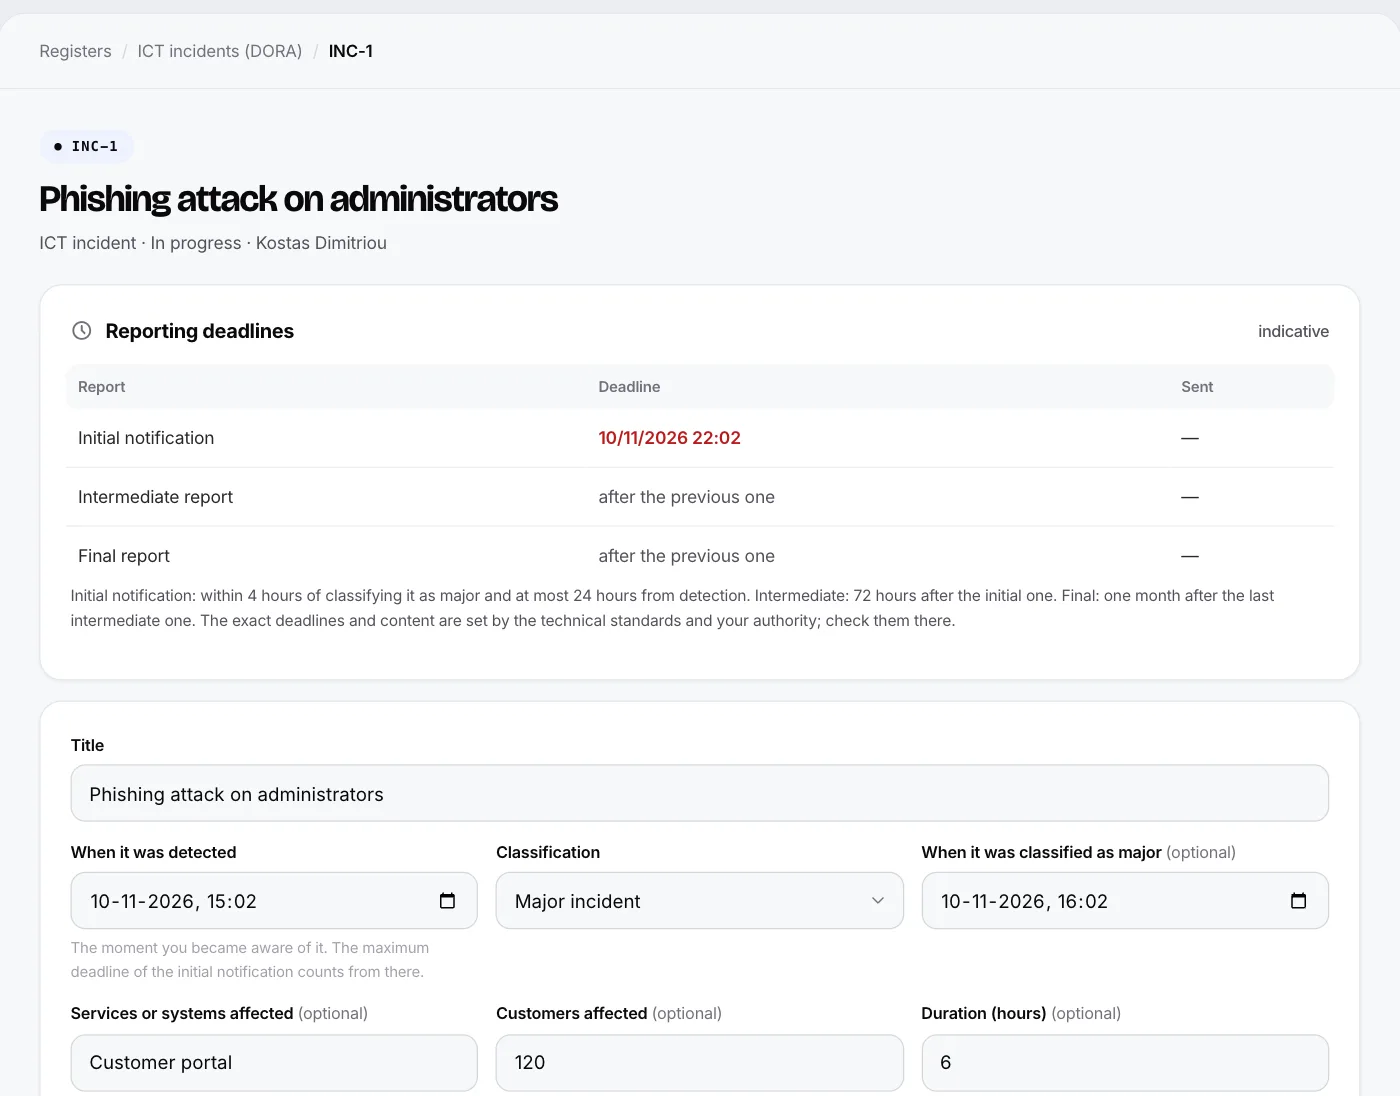
Classification, initial, intermediate and final report. For every major incident the deadlines are calculated and go into the calendar.
Third-party ICT providers
A register of information with subcontractors and data locations, contract clauses, concentration risk and exit plans.
Your provider register, ready from the start.
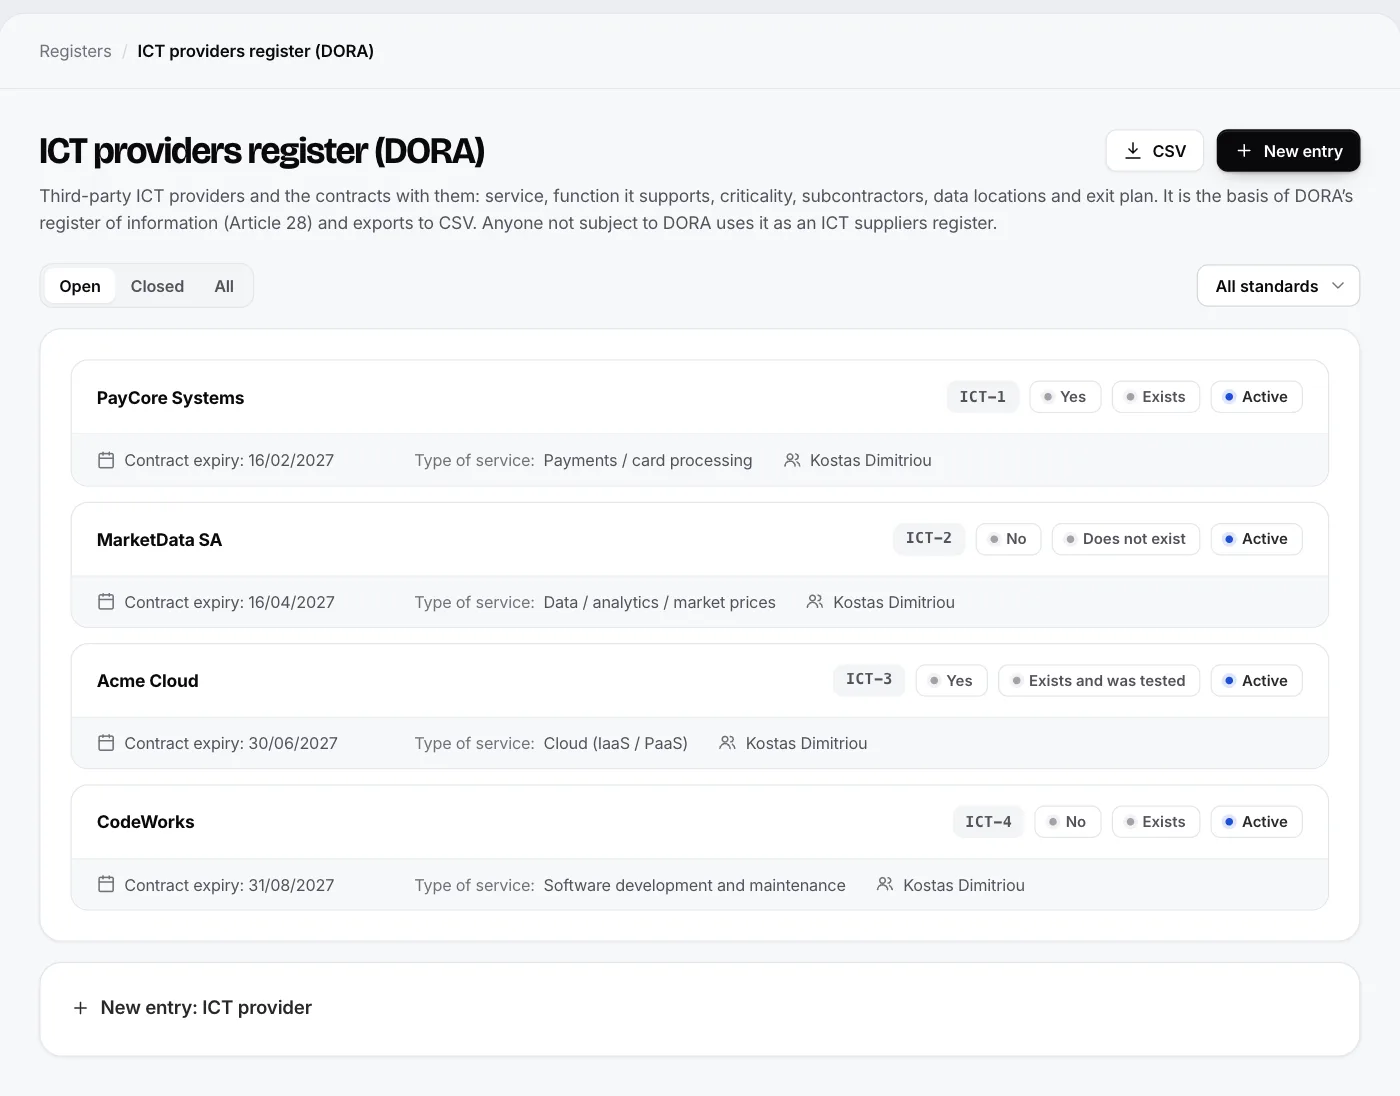
Each provider with its service, the function it supports, whether it is critical, its subcontractors, the data countries and the exit plan. The contract expiry goes into the calendar and the whole register exports to CSV.
If DORA does not apply to you, the same register works for your ICT suppliers.
Together with the ISOs, without double work
Policy, document control, internal audit and management review are shared with ISO 27001 and ISO 22301. In the integrated system you cover them once.
A starting point, not legal advice
The questions are our own, with references to the articles. They do not replace the technical standards (RTS and ITS) or the guidance of your supervisory authority. For the final judgement, turn to a lawyer or consultant.
Questions about DORA.
01Does DORA apply to me?
It applies to financial entities and their ICT providers. Some entities are exempt, such as small insurance intermediaries. The first section of the questionnaire helps you record that.
02Do you submit the reports to the authority?
No. COMPLIANT.GR is the place where you organise incidents, providers and deadlines. You make the submission yourself through your authority’s channel.
03I am an ICT provider, not a bank. Is it for me?
Yes. You declare that you are a provider and you get the section on clauses, incident notification, client audit and exit, which your financial clients ask for.
04Which plan do I need?
DORA, the registers and the integrated system are included in the Pro and Business plans. The “ESG, ESPA or ISO” plan does not include them.
See how the processes and registers work.
In the demo you enter a company with ISO 27001, ESG and ESPA, with registers, actions and audits. It is yours for three days.